PDPA Audit Checklist for Malaysian Websites & Apps (2026 Update)
- 19 February 2026
- Technology
Key Takeaways
- Silence is no longer consent; implied consent via “continued browsing” is risky under new amendments.
- Pre-ticked boxes are illegal for sensitive data and highly dangerous for standard marketing consents.
- Overseas hosting (AWS/Google) requires verified “substantially similar” laws or specific contracts.
- Privacy Policies must be bilingual (Bahasa Malaysia and English) to be legally valid.
- Data retention is not forever; you must have a schedule to permanently delete inactive user data.
Is your business website actually illegal under the new Act 854 and PDPA 2024 amendments?
If you are still using pre-ticked consent boxes, lack a bilingual Privacy Policy, or host data overseas without a specific contract, your site is likely non-compliant. The 2025 amendments introduced stricter liability for data processors and fines up to RM1 million, meaning “standard” web practices from 2023 are now financial liabilities.
We’ve all seen them—those annoying “Accept All Cookies” pop-ups. You might think they are just a Western “GDPR thing,” but the game has changed in Malaysia. With the new fines effectively doubling or tripling the financial risk, treating customer data casually is no longer just “bad practice”—it’s a direct threat to your cash flow.
This guide cuts through the legal jargon to give you a practical, hands-on audit checklist. We will cover exactly what needs to change on your website, app, and backend storage to keep the Jabatan Perlindungan Data Peribadi (JPDP) happy.
🧾 Compliant vs. Risky Website Features
Feature | ✅ Compliant Approach (Safe) | ❌ Risky / Non-Compliant Approach | Potential Penalty |
Cookie Banner | Active “Opt-In” buttons (Accept/Reject). Detailed policy link. | “By using this site, you agree…” (Implied) or No banner at all. | Fines & Loss of Trust |
Sign-Up Forms | Empty checkboxes requiring user to click to agree to T&C/Marketing. | Pre-ticked boxes (✅) that force users to uncheck to opt-out. | Illegal (Invalid Consent) |
Privacy Policy | Available in both Bahasa Malaysia and English. | English-only policy; Generic “Lorem Ipsum” template. | RM300k+ Fine / Jail |
Data Storage | Cloud provider with contract/guarantee of PDPA compliance (e.g., local region or standard clauses). | Cheap overseas hosting with no data protection agreement. | Breach of Transfer Rules |
Data Retention | Auto-delete mechanism for inactive accounts (e.g., after 24 months). | Hoarding data forever “just in case.” | Breach of Retention Principle |
Do I Really Need a “Cookie Banner” in Malaysia?
The “Notice and Choice” principle creates a de facto requirement.
Technically, the PDPA doesn’t say the words “Cookie Banner.” However, it does mandate the Notice and Choice Principle. You must inform users that you are collecting data (Notice) and give them the option to agree or disagree (Choice).
Since cookies often collect IP addresses and browsing behavior—which can be linked to identify an individual—they fall under “Personal Data.” The 2025 amendments strengthened the need for explicit consent, especially for tracking and marketing cookies.
- The Verdict: If you use Facebook Pixel, Google Analytics, or any tracking tools, you must have a banner. A simple “We use cookies” footer is risky. Use a banner that asks for an “Accept” click.
Are Pre-Ticked Consent Boxes Illegal Now?
The era of “accidental consent” is over.
For years, Malaysian marketers loved the pre-ticked box. You know the one: you sign up for a newsletter, and the “I agree to receive marketing emails” box is already checked.
Under the updated guidelines and the stricter interpretation of Section 6 (General Principle), consent must be a voluntary and positive action. A pre-ticked box is considered “passive” or “implied” consent, which does not hold up well in court, especially if sensitive data is involved.
- The Fix: ALL checkboxes on your forms (Contact Us, Checkout, Registration) must start empty. The user must physically click to check them. This proves they read and agreed to the terms.
Can I Host Customer Data on Overseas Servers?
The “Whitelist” is dead; Contracts are King.
Previously, we waited for a government “Whitelist” of safe countries to store data. That list never really happened. The new amendments have scrapped the whitelist concept in favor of a more practical (but stricter) rule: Accountability.
You can transfer data to AWS, Google Cloud, or Azure servers in Singapore, the US, or Japan IF:
- The country has “substantially similar” data laws to Malaysia.
- OR (More commonly) You have a contract with the provider that ensures they protect the data to PDPA standards.
- The Trap: Using cheap, budget hosting in countries with weak data laws (or no laws) without any service agreement. If that server gets hacked, you are liable for the cross-border breach.
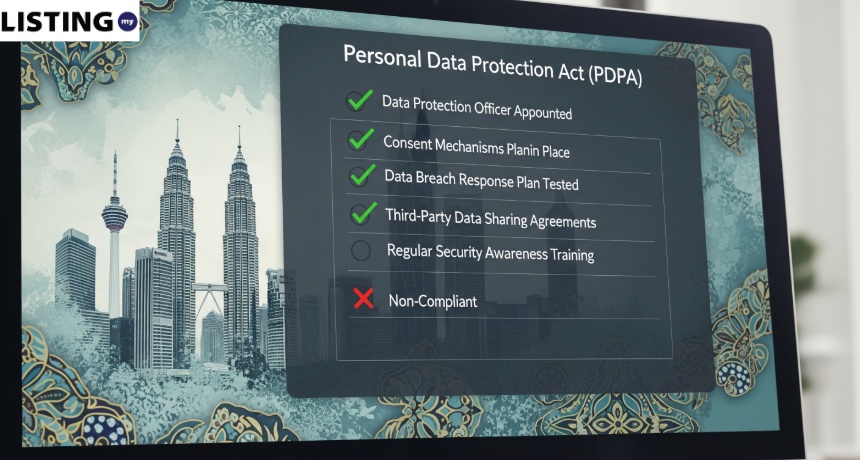
What Is the Ultimate PDPA Audit Checklist for 2026?
A practical 10-point inspection for your digital assets.
If you can tick off all 10 items below, your SME is in the top 10% of compliant Malaysian businesses.
1. The Bilingual Policy Check
Does your website have a Privacy Policy visible in both Bahasa Malaysia and English?
- Requirement: Mandatory under PDPA.
- Action: Translate your policy immediately. Do not use Google Translate; get a proper legal translation.
2. The “Contact Us” Form Audit
Look at your enquiry forms. Is there a link to the Privacy Notice before the submit button?
- Requirement: Notice Principle.
- Action: Add a sentence: “By submitting this form, you agree to our Privacy Policy.”
3. The “Empty Box” Rule
Check your checkout and newsletter sign-ups. Are any boxes pre-ticked?
- Requirement: Valid Consent.
- Action: Uncheck them by default in your website code.
4. SSL Encryption (HTTPS)
Is your site loading with a secure padlock icon?
- Requirement: Security Principle.
- Action: Install an SSL certificate. Unsecured HTTP sites processing data are a blatant violation.
5. The “Unsubscribe” Link Test
Send a test newsletter to yourself. Is the “Unsubscribe” link easy to find and working instantly?
- Requirement: Right to Withdraw Consent.
- Action: Ensure 1-click removal works.
6. Cloud Storage Location
Where is your database actually hosted? (e.g., AWS us-east-1).
- Requirement: Cross-border Transfer standards.
- Action: Verify your cloud provider’s Data Processing Agreement (DPA) covers Malaysian PDPA requirements.
7. Data Retention Schedule
Do you have customer data from 2015 that hasn’t been touched?
- Requirement: Retention Principle.
- Action: Delete inactive user data older than 7 years (tax records) or 24 months (inactive leads).
8. Employee Access Levels
Does your intern have “Admin” access to the entire customer database?
- Requirement: Security Principle.
- Action: Limit access. Only give staff access to the data they need to do their job.
9. Vendor Vetting
Do you share data with a third-party logistics (3PL) or marketing agency?
- Requirement: Data Processor Liability.
- Action: Sign a data protection agreement with them. You are responsible if they leak your data.
10. The Breach Button
If your site gets hacked tonight, do you know who to call?
- Requirement: Breach Notification (Mandatory by June 2025).
- Action: Draft a “Breach Response Plan” listing the JPDP hotline and your IT support contact.
Need Expert Help?
Struggling with compliance? Connect with verified IT and legal experts on Listing.my, the trusted business directory helping Malaysian SMEs grow securely.
Conclusion: Compliance is Cheaper Than a Breach
The updates to the PDPA and the Cyber Security Act 2024 aren’t meant to kill your business; they are there to force digital maturity. A clean, compliant website builds trust. When a Malaysian customer sees a bilingual privacy policy and a clear “Opt-In” mechanism, they know you are a professional entity, not a fly-by-night scam.
Start with the Empty Box Rule and the Bilingual Policy—these are the two most visible red flags that enforcement officers look for.